At our sample company, the AI answered 61 of a bank’s 64 security questions straight from the record.
That was one week of the month we followed at a made-up company. A feature list only tells you so much about compliance software, so here’s the work itself, story by story.
Every app screen below is Kanonik’s own, filled with the sample company’s data. If you’d rather ask than read, Ask Kanonik answers a few sample questions about the same company, from what its team approved.
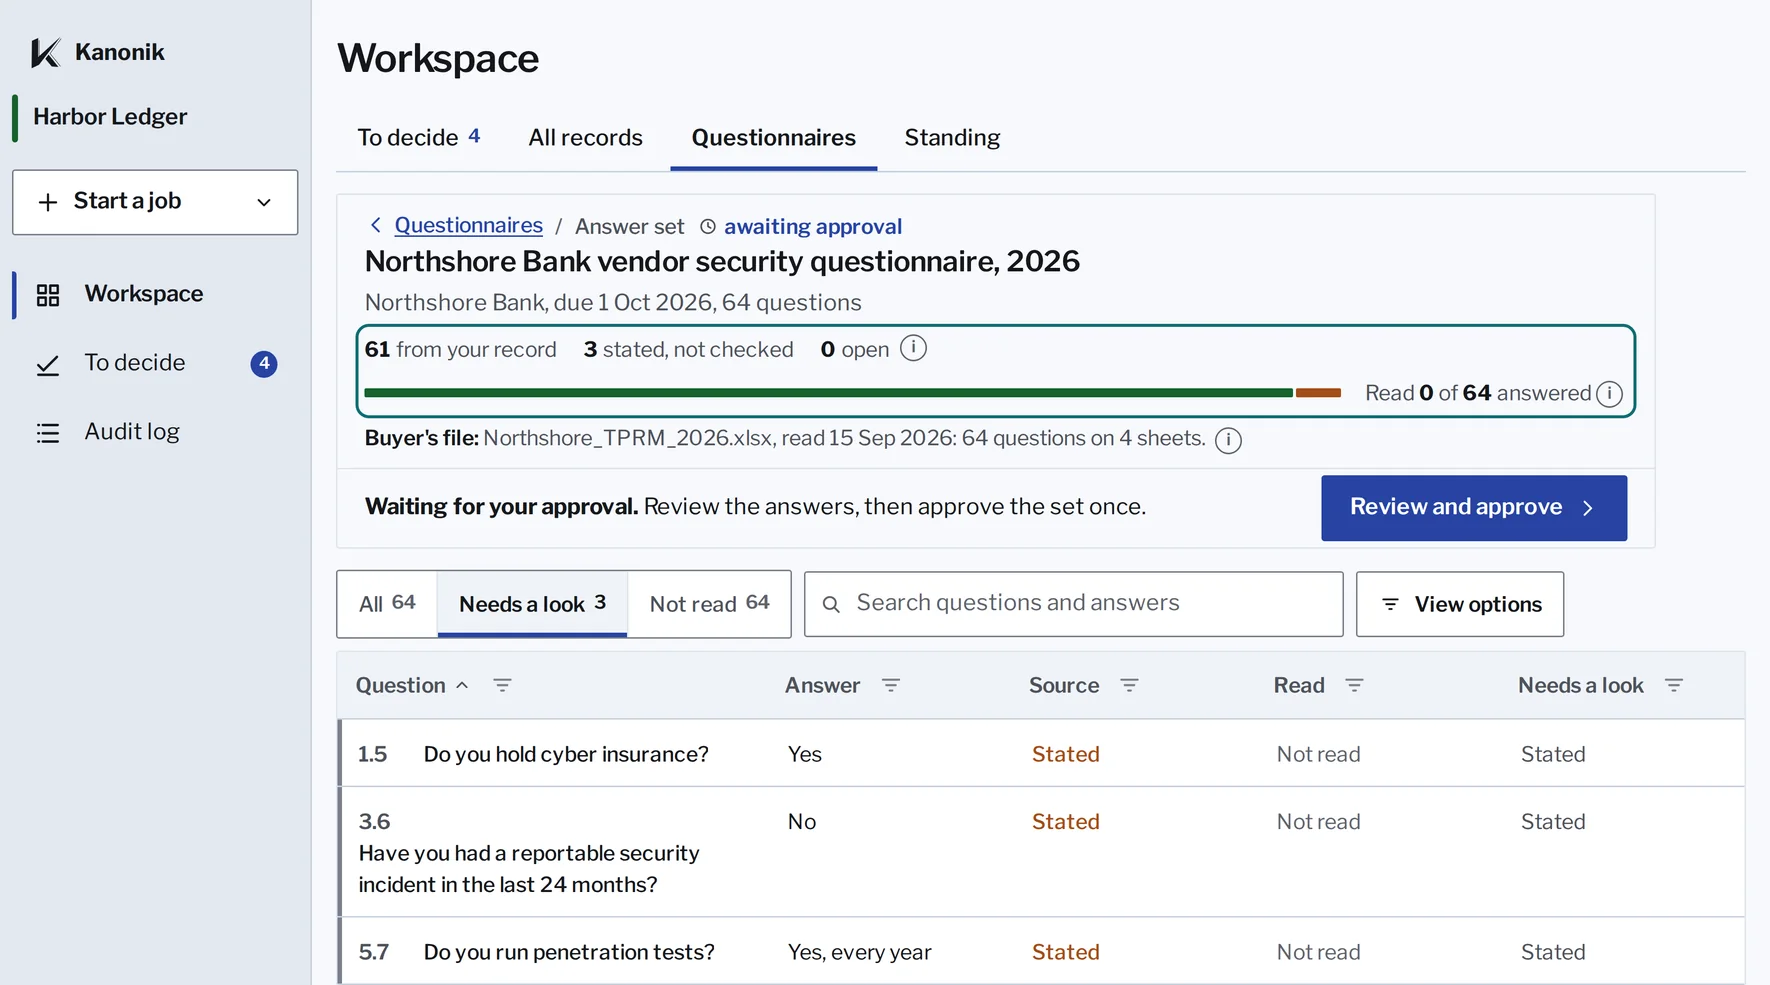
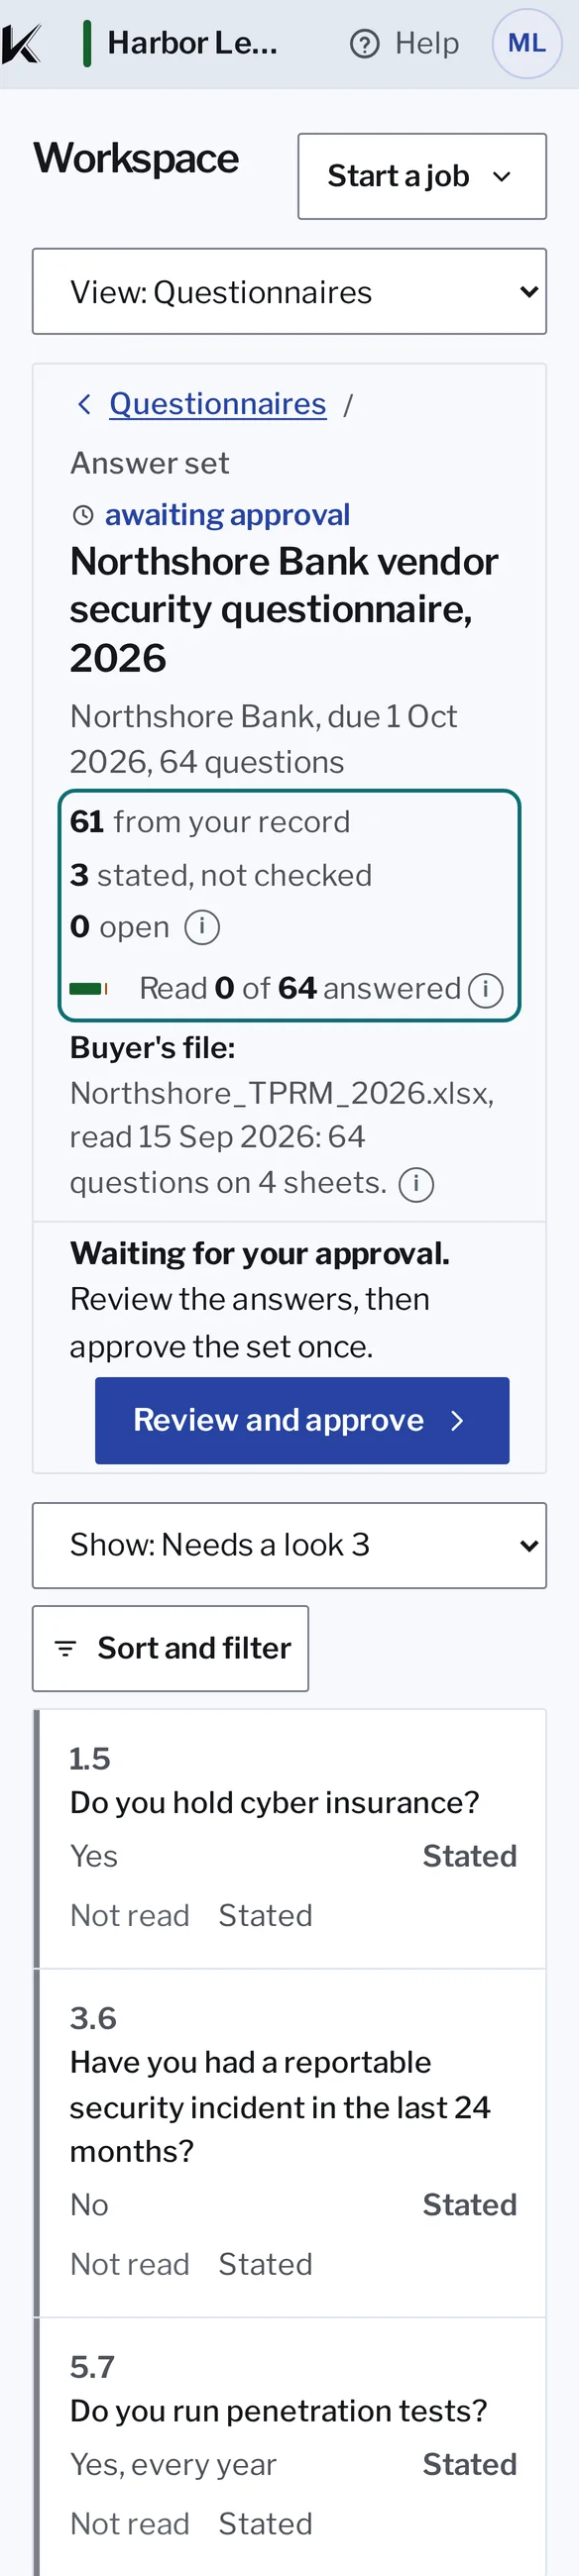
Three answers are marked as stated, with no record behind them.
Questionnaires in Kanonik, with sample data from Harbor Ledger.
Harbor Ledger is the sample company in all our examples.
It’s a 40-person fintech, and it’s made up. Its ledger and payments API run on Amazon Web Services.
Here are four of the people who use Kanonik there:
Dana Reyes
runs security and is the workspace admin. She works in Claude Desktop.
Sam Okafor
is a reviewer, so he can confirm other people’s work. He uses ChatGPT.
Mei Lin
is an author. She drafts with Claude Desktop, and her policies and controls wait for Dana or Sam to confirm them.
Priya Shah
of Shah Assurance is the auditor for Harbor Ledger’s SOC 2 readiness review, ahead of the audit in December. She can read the approved record, and she can’t edit or approve anything in it.
Here’s the rule you’ll see in every story. Whoever’s AI drafted something accepts it first. That’s them saying they’ve read what their AI wrote.
Questionnaire answers, risks, evidence and fixes need only one person. Whoever drafted one can record it alone. And a company with only one person who can approve isn’t stuck. That person approves alone, and the record says no second reviewer was there.
15 to 17 September
Mei finished Northshore Bank’s 64 questions two weeks early.
If you sell to banks, you know the questionnaire. Northshore Bank’s arrived on 15 September. It had 64 questions over four sheets of a spreadsheet, due on 1 October.
Mei gave it to her AI. Each answer it wrote quoted a record the team had already approved, with the source beside it. Sixty-one came out that way. The other three were things only Harbor Ledger could say, like the limit on its cyber insurance, and Kanonik marked them as stated, with no record behind them. Nothing was left open.
Mei read the set and approved it herself on 17 September, two weeks before the deadline. Answers need only one person, so her approval put the set on the record. She can download it in the bank’s own format and send it back.
We save every answer in the set, so the next buyer’s questions start from them. If a saved answer goes stale, Kanonik flags it. We think every questionnaire should be easier than the one before.
25 September
Two of the answers to Brightwater’s 14 questions disagreed.
Brightwater Payments is about to sign a card-issuing contract with Harbor Ledger. First it sent 14 security questions, due on 2 October.
Dana pasted the spreadsheet into Claude Desktop. Ten answers came from the record. Two were Harbor Ledger’s own statements, about its cyber insurance and its incident history, and Kanonik marked them that way. Two stayed open, because nothing on the record covered them. Brightwater wanted a SOC 2 Type II report, and there was no penetration test on the record.
Then Dana’s AI flagged something worse than a gap. Question 4.3 said admin access is reviewed every six months, under version 1.2 of the access control policy. Question 7.1 said every quarter, citing the quarterly access review Sam recorded on 18 September, which removed 2 of 23 admin accounts.
Kanonik put the two answers side by side and held the approval. Dana can’t approve the set while they disagree, and Kanonik’s server won’t take it either.
We hold it on purpose. A buyer who finds two answers to the same question starts doubting the other twelve.
Nothing has gone to Brightwater yet, and Dana has a week to put it right.
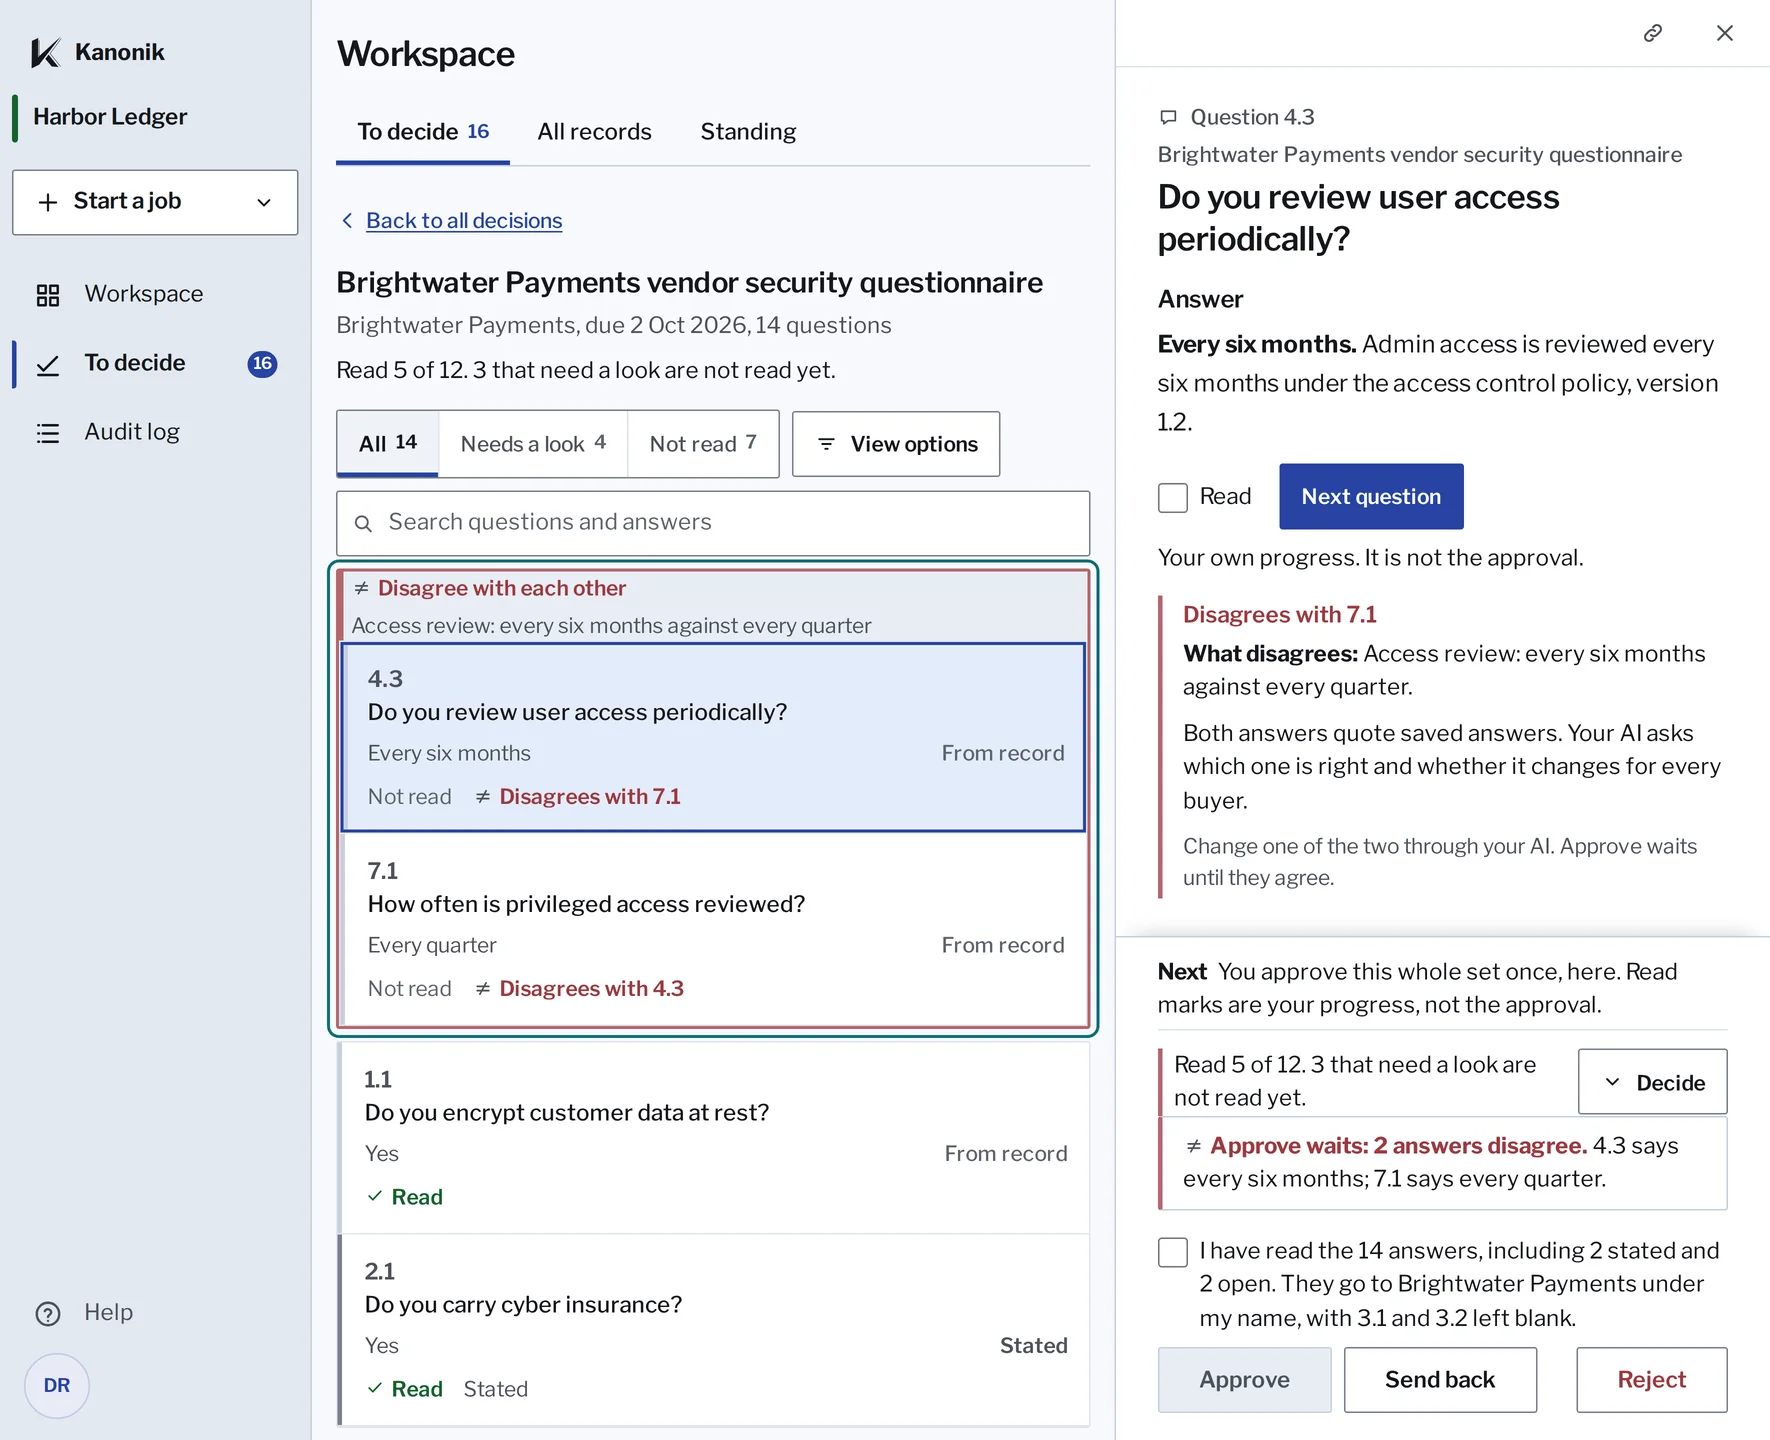
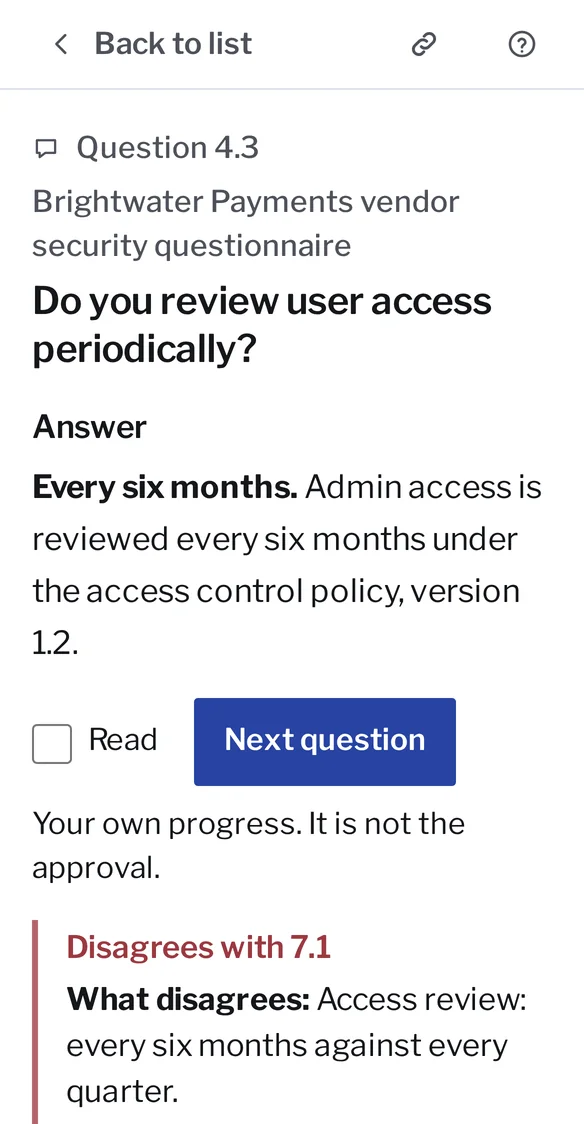
Approval is held until the two answers agree.
Kanonik’s To decide screen, with sample data from Harbor Ledger.
Here’s what else happened at Harbor Ledger in September.
- Priya
Priya’s readiness review found a gap in how people leave.
1 to 25 September
Dana invited Priya Shah, Harbor Ledger’s auditor, into the workspace with access until 31 December. Priya checked a Proof Snapshot of the record on her own laptop and found two leaver tickets closed with no record that GitHub access was removed. Dana’s AI drafted the fix with the proof attached, and it waits for Dana.
- Dana
Dana’s new access policy waits for Sam’s signature.
25 September
Version 1.2 of the access policy still said admin access is reviewed every six months. Dana’s AI brought it up to date, the check passed it and Dana accepted it. It waits for Sam now, because a policy needs a second person, and whoever drafted it can’t be the one who confirms it.
- Dana’s AI
Brightwater’s contract names SOC 2, so that’s the report Harbor Ledger will give it.
24 and 25 September
Brightwater’s draft contract asks for a SOC 2 Type II report every year. Dana’s AI recorded that as an obligation and proposed giving Brightwater the SOC 2 report. Harbor Ledger works to ISO 27001 as well, and the AI also wrote down why it didn’t offer that instead. The company is further along on SOC 2, so ISO 27001 would take longer to reach.
- Mei
Mei sent a control back to her AI with a note.
25 September
Kanonik’s check passed Mei’s access review control, but the control gave unconfirmed accounts five working days, and the access policy says one. Mei sent it back with that note. Her AI changed the line, and she accepted the new version.
- Foresight
A new backup vendor was checked before anyone signed.
September
Engineering wanted to move backups to another provider. Foresight found that its contract would break three of Harbor Ledger’s promises to customers, including the one about keeping data in the EU.