How Kanonik works
This is the path one draft takes from your AI to an entry your auditor can check.
Then we make our case for bringing your own AI, and show you how we build Kanonik.
Five stops between your AI and your Record
Your AI
Drafts in Claude, ChatGPT or another assistant, signed in as you.
Kanonik’s server
Checks who’s calling and turns the call into a proposal.
The Verifier
Fixed rules first, then an AI reviewer, with a verdict and its reasons.
Named approval
A named person approves in Kanonik itself, from a one-time link.
The Record
Sealed and chained, so any change shows.
Your AI reaches your systems through its own connections. Kanonik never signs in to them or holds the keys.
Follow one draft
Dana asks her AI to tighten the access policy. Here is every stop between that chat and her record.
Your AI
Your AI writes the draft
Dana asks in her own chat, signed in as herself. Her AI writes the policy and calls Kanonik.
Dana Reyes
Update our access control policy: quarterly access reviews and hardware keys for admins.
kanonik propose_policyWho may reach what policy, version 2.0
What Kanonik sent back to your AI
- verdict.passed
- true
Draft preview only. Nothing is committed to the tenant’s record and no approval exists yet: a draft id was minted and the rule-tier check ran, but this is not on the hash chain.
Kanonik’s server
Kanonik checks who’s calling
The call becomes a proposal. Nothing on the record changes.
Kanonik checks
- Who’s calling
- Dana Reyes, through her AI
- Workspace
- Harbor Ledger
- Role
- Admin
- Logged
- The call and Kanonik’s answer
On your record
Who may reach what policy
Version 1.2, in force. Recorded 12 Mar 2026.
Proposed
Who may reach what policyDraft
Version 2.0, replaces 1.2.
Checks run when it is sent for approval.
The Verifier
The Verifier reads it twice
Fixed rules first, with no model. Then an AI reviewer. Your AI has no tool to skip either.
Fixed rules
No model is involved.
kanonik.policy.placeholder-content-detectionNo TBD or [DATE] left in the textkanonik.policy.body-length-minLong enough to be a real policy
A draft that still said [DATE] would be refused here, and the AI reviewer would never see it.
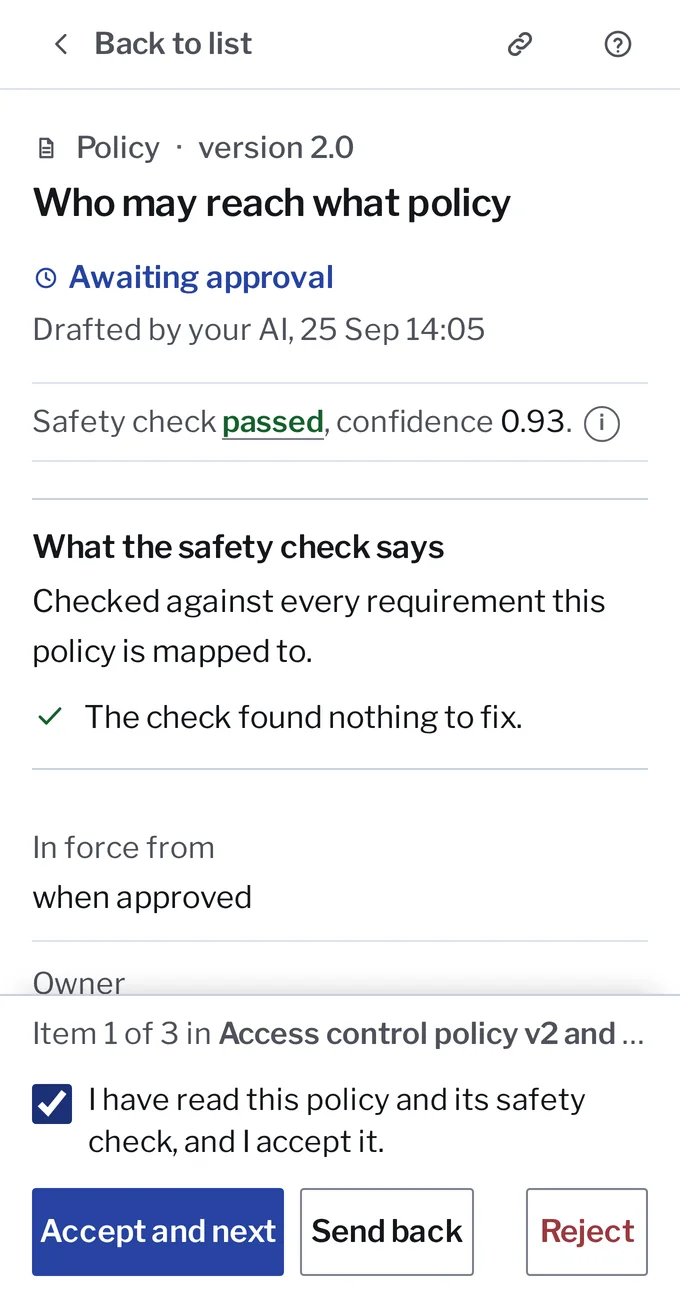
What the safety check says
Safety check passed, confidence 0.93.
Checked against every requirement this policy is mapped to.
The check found nothing to fix.
A pass records nothing on its own.
Named approval
Named people approve
Dana opens a link that works once and accepts. A policy needs a second person, so Sam confirms.
Dana, from her one-time link
In the request: Access control policy v2 and two applicability decisions
Who may reach what policy
Reviewed every six months quarter. Admin access requires a hardware security key.
I have read this policy and its safety check, and I accept it.
Accept and next
An approval link works once, for one hour, and only Dana’s sign-in opens it.
Then Sam, because a policy needs a second person
Who may reach what policy
I have read this policy, its acceptance by Dana and the safety check.
Confirm
Accepted by Dana Reyes, confirmed by Sam Okafor.
The Record
It joins the Record
Each entry carries the hash of the one before it. If an old one is edited, the hashes stop matching.
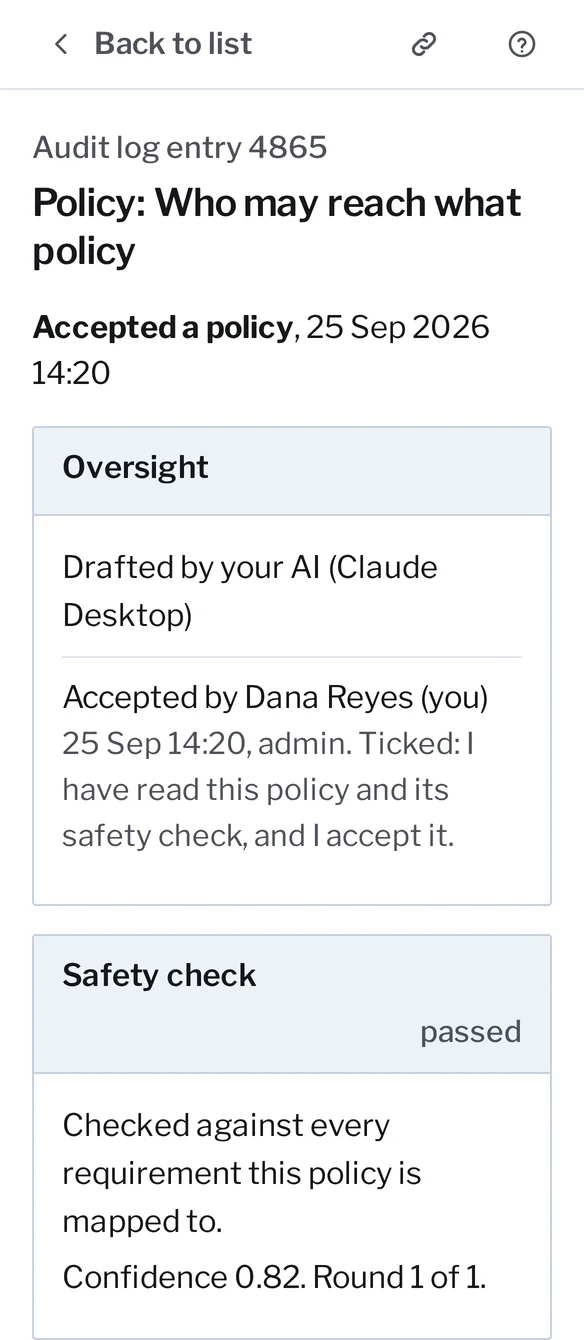
Audit log entry 4864
- Entry hash
- 57cb87ce...905b
Audit log entry 4865
Accepted a policy, 25 Sep 14:20. Dana Reyes ticked: I have read this policy and its safety check, and I accept it.
- Previous entry
- Audit log entry 4864
- Previous hash
- 57cb87ce...905b
- Entry hash
- 58cb8961...8f5a
Signed on a schedule
Sam’s confirmation joins next, as its own entry. Then version 2.0 is the policy on your record. Kanonik signs the latest entry on a schedule.
Your AI
The AI side
Skills that make your AI a compliance specialist
When your AI connects, it loads Kanonik’s signed, plain-text skills for policy writing, control assessment, narrative writing, audit readiness, risk discovery, a GRC lead and the weekly digest. None grants a permission the AI didn’t already have, and because they’re signed, an audit narrative can show which skill version produced it.
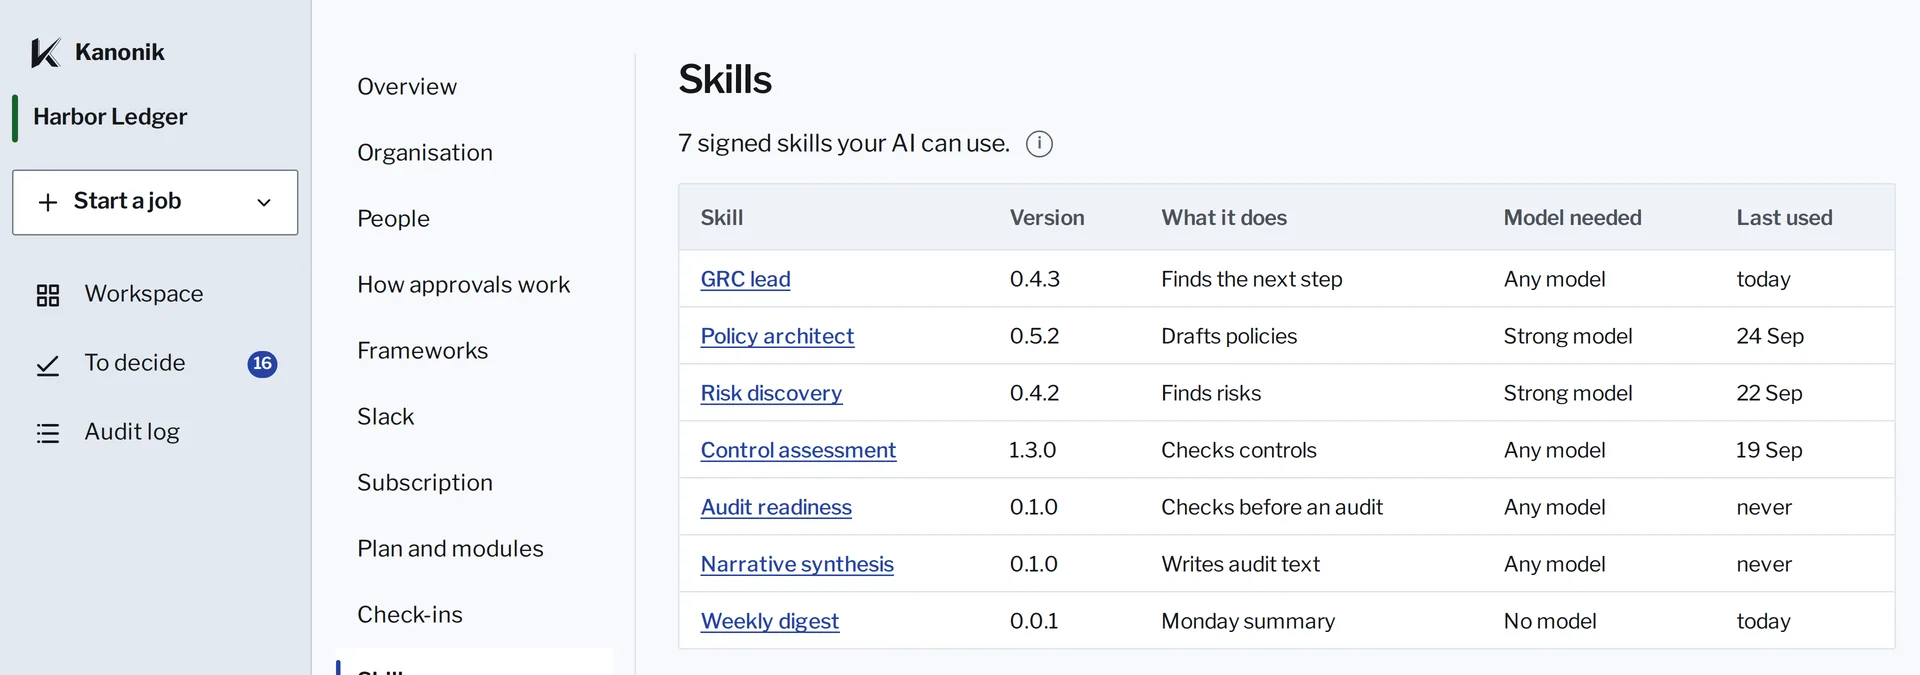
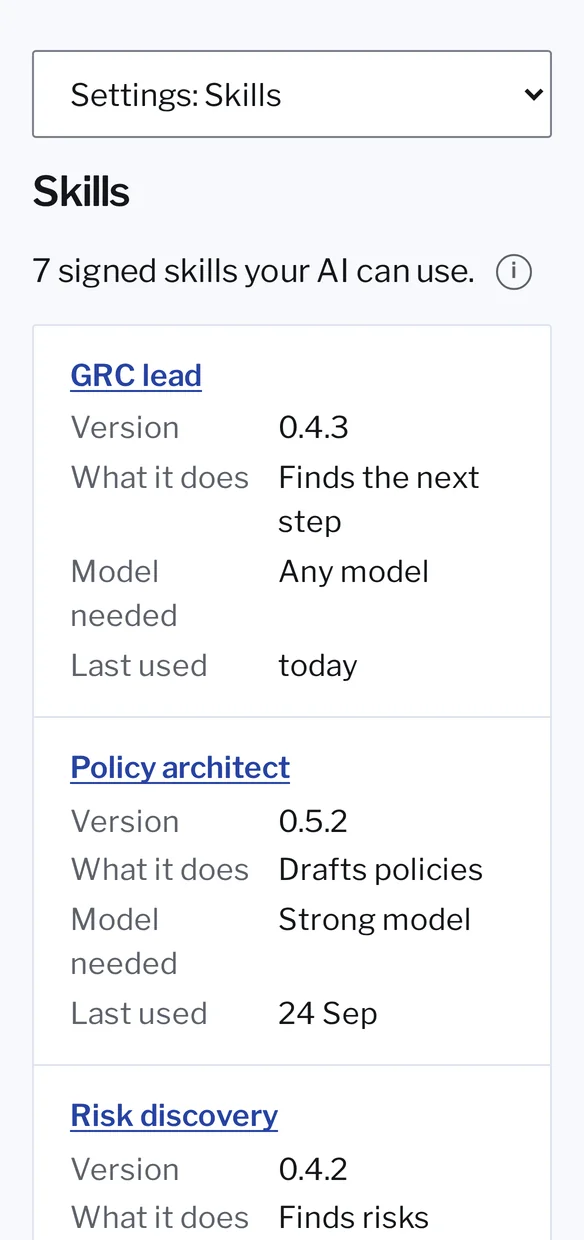
Kanonik’s screens, with sample data.
Connect any AI
Add Kanonik as a connector in Claude, ChatGPT or another assistant and sign in with your own Kanonik account. Your AI can then do in Kanonik what your role allows, and nothing more.
Your AI’s own connections
Your team gave your AI its connections to GitHub or your cloud account, and you can switch them off at any time. Kanonik never signs in to those systems or holds the keys. It only receives what your AI drafts.
A draft is only a proposal
Every call reaches Kanonik’s server first, which checks who’s calling, from which workspace and with what role, and logs the call and response. Calling a record tool creates a proposal, and your current policy, controls and evidence stay as they are until a person approves.
The checking side
The Verifier runs on Kanonik’s servers whenever a proposal is saved, and the AI has no tool of its own to skip it. It reads every draft twice.
Fixed rules come first
No model is involved, so a policy that still says TBD or has a [DATE] blank is refused.
Then an AI reviewer
An AI reviewer that Kanonik runs checks the draft against the requirements it should meet.
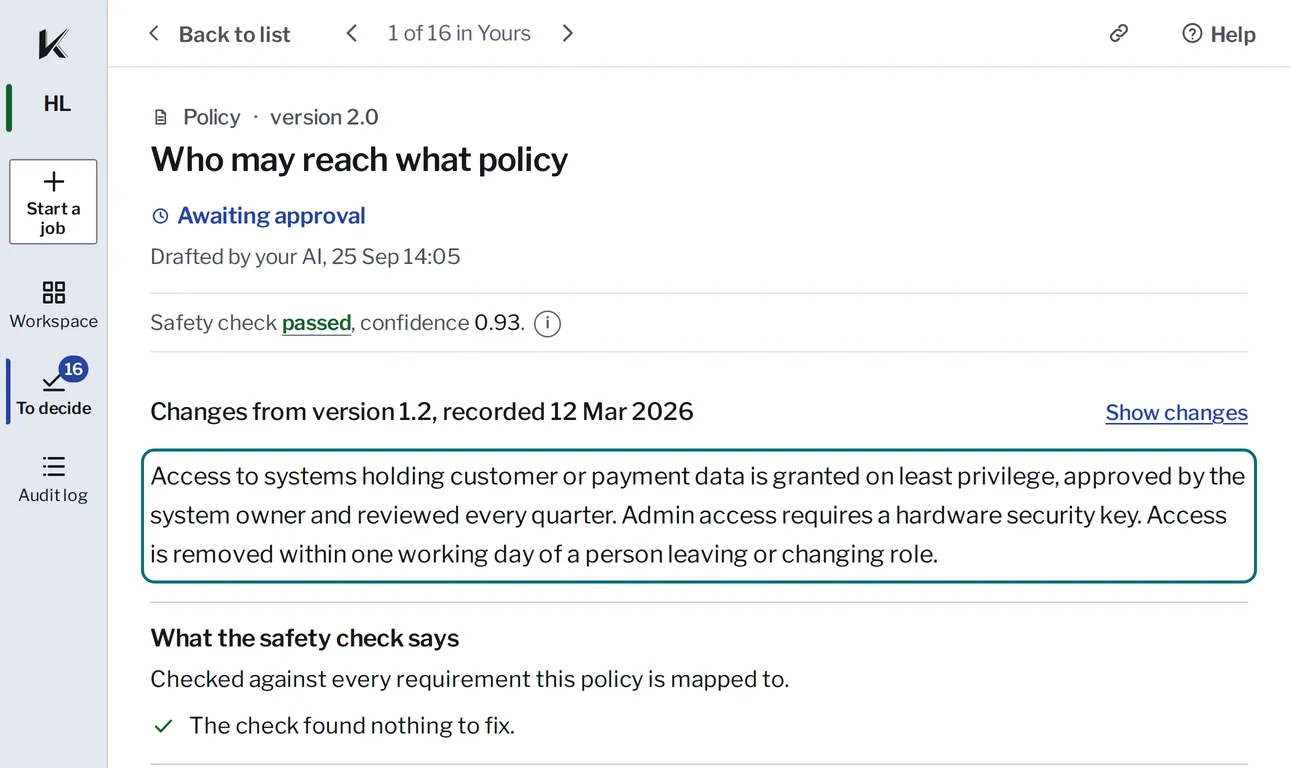
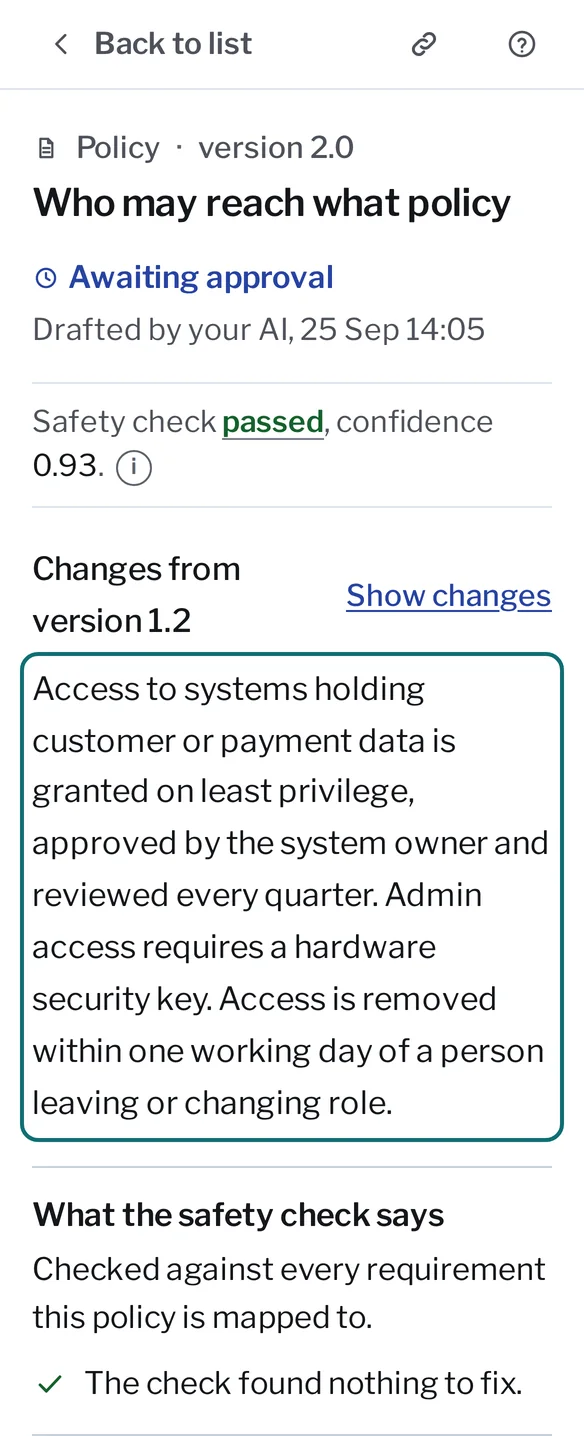
What changed is marked, and the check’s result sits on the draft.
To decide in Kanonik, with sample data from Harbor Ledger.
Every AI decision is logged with its inputs, the model used, a confidence score and the reasoning. If a draft falls short, it goes back to your AI to rewrite before anyone is asked to read it. If the Verifier isn’t sure, the draft waits in a review queue. And a pass doesn’t record anything on its own.
Assistants tend to get one detail wrong, the one your auditor would find, and the Verifier finds it first.
The approval side
Once a batch passes the checks, the approver gets one request for all of it, as a link that works once. It arrives by email or in their AI chat, and a notice in Slack tells them it’s waiting. They open it in the Kanonik web app, signed in as themselves. We don’t accept an approval typed into a chat, because anyone at the keyboard can type “yes”, and so can the AI.
Each item shows what changed and what the Verifier found. Accept stays off until the approver ticks that they’ve read both, and the tick is kept with the decision in the Audit log. A send-back note in the approver’s own words goes to the AI for its next pass, and the server refuses to write anything without a named person’s approval.
Dana
Each draft shows what changed and what the check found. Tick that you’ve read it, then accept.
Kanonik
When you accept, the decision becomes an Audit log entry with your tick on it. Sam confirms next.
Dana
Each draft shows what changed and what the check found. Tick that you’ve read it, then accept.
Kanonik
When you accept, the decision becomes an Audit log entry with your tick on it. Sam confirms next.
Approving in Kanonik, with sample data from Harbor Ledger. It plays once; then it’s yours to click through.
The second person
Once someone else can approve, policies and controls wait for a second person, with no deadline, while evidence and vendor entries can be approved by whoever drafted them.
Working alone
A solo user ticks a second box that reads “I am the only person in this workspace, and I am sealing my own governance item,” and Kanonik records it as a named exception your auditor finds in the package. Other exceptions to the rule are granted for a set time and expire.
The Record side
Each approved entry carries its owner, date, source and approver, plus a hash of its own contents and of the entry before it. If someone edits an old entry, the hashes stop matching from there on. The database refuses edits and deletes, so a correction is a new entry pointing back to the old one, and Check the chain in the Audit log confirms the links hold.
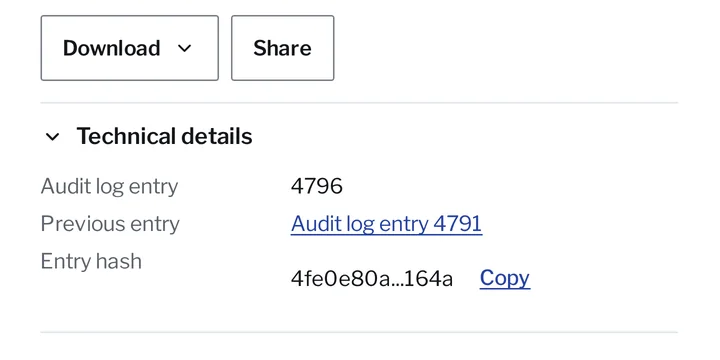
Each entry carries the hash of the one before it. Check the chain says whether they still match.
The Audit log in Kanonik, with sample data from Harbor Ledger.
Two dates on every entry
Each entry records when it took effect and when it was recorded, and the two differ when something is recorded late. Kanonik answers both auditor questions, what was in place on 30 June and what the Record said that day, and your AI can ask them too.
Proof you can check yourself
The Sealed Audit Package holds every decision and its approver, ships with its own checkers (verify.html, verify.py and verify.mjs), needs no network or Kanonik account, and fails if one byte has changed. At kanonik.ai/verify, you or anyone you send it to can check a code or a file in the browser with nothing uploaded.
Bring your own AI
The newest model, the day it ships
Switch to a better frontier model the day it’s out, with no lock-in. Your Record doesn’t move.
It fits your procurement
Use the AI your organization already approved and governs. Kanonik charges no AI fees.
Built on frontier AI
We put the frontier labs’ models to work instead of pretending to out-build them.
No way into your network
Kanonik never gets into your network. The only credential involved is your Kanonik sign-in.
No connector sprawl
We don’t run hundreds of custom connectors, because every one of them is a weak spot someone has to maintain. The AI reaches your systems through connections it already has.
We had no old product to carry, so we built Kanonik around AI from the start. Every time the frontier models get better, Kanonik gets better with them.
Our own security
Built to NIST SP 800-53
We’ve built Kanonik to NIST SP 800-53, the control set FedRAMP is built on, since the first commit.
- Signed container images, with an SBOM for every build
- Mutual TLS between application services
- Infrastructure as code, deployed through GitOps
- An append-only audit log, with approved changes on a signed hash chain
Private deployment on Enterprise
Enterprise runs Kanonik in your own cloud account or data center, so the Record stays on your own servers.
Try it on a real policy
Start the trial, connect your AI and ask for a policy you actually need. Once it’s approved, press Check the chain in your Audit log. You start with a card. No sales call, no setup project.